Continuous Penetration Testing
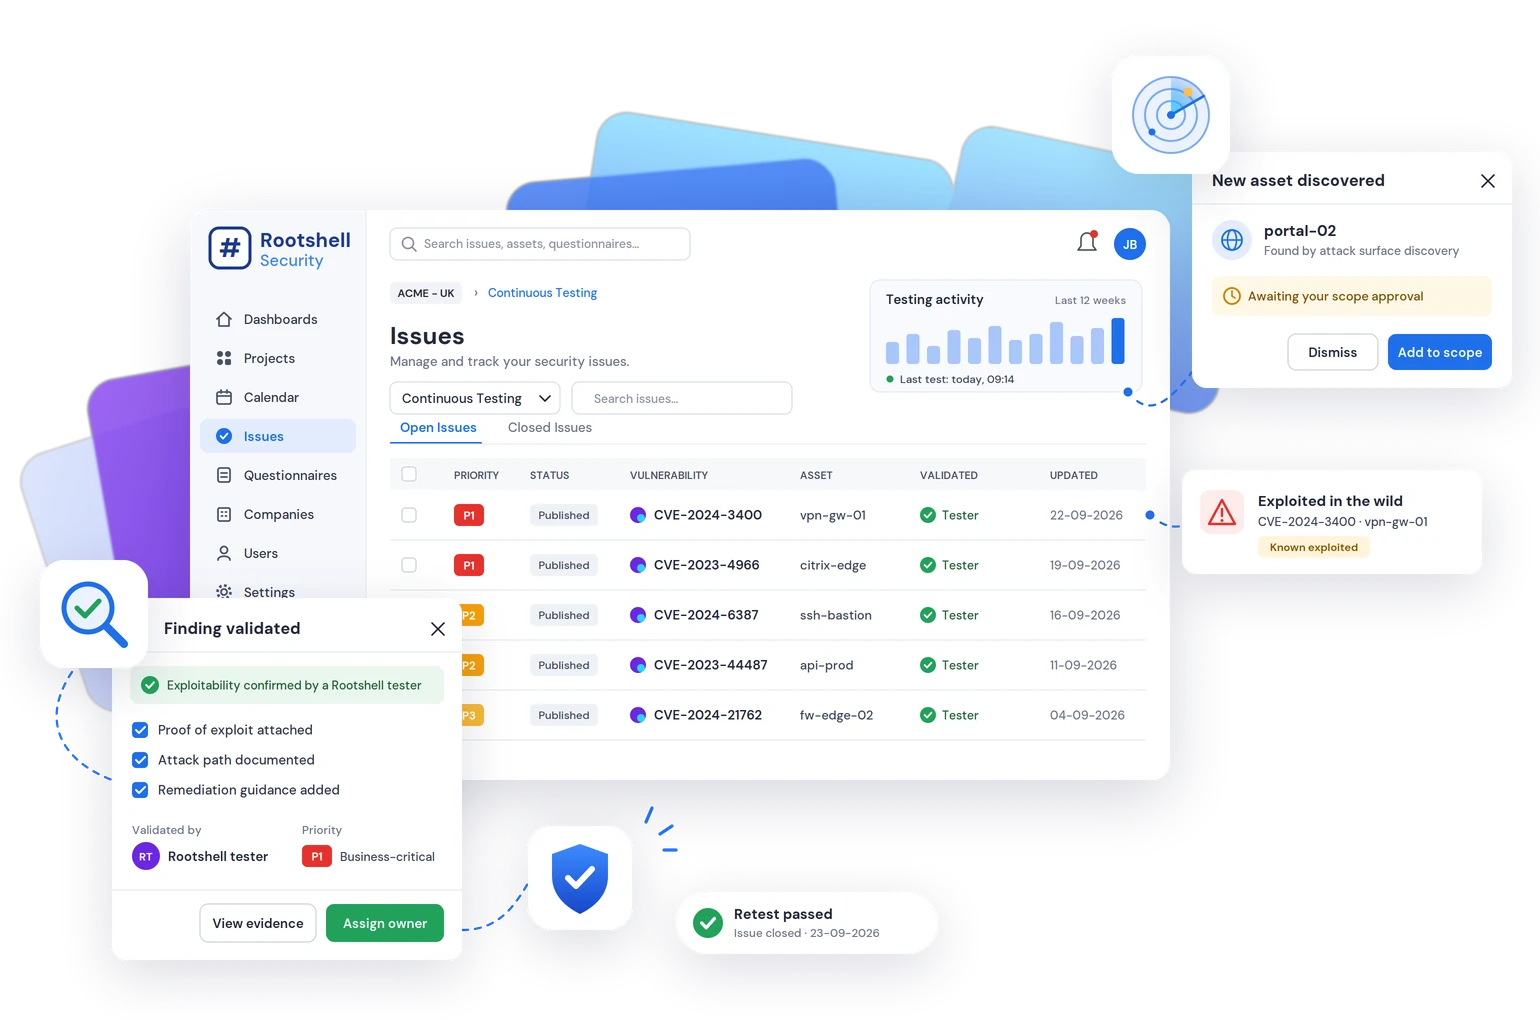
Rootshell combines expert-led penetration testing, attack surface visibility, automated discovery, and remediation tracking through the Rootshell Platform.
The result is a continuous testing model that helps security teams reduce exposure faster, prove progress more clearly, and stop relying on static reports and spreadsheets.
Join 1,000+ leading companies who trust Rootshell Security



Why Continuous Penetration Testing Matters
Traditional penetration testing still has its place, but most organizations no longer operate in fixed, predictable environments. New assets appear, applications change, vulnerabilities are disclosed constantly, and attacker behavior evolves faster than annual testing cycles can keep up with. Modern cybersecurity frameworks such as the NIST Cybersecurity Framework emphasize the importance of continuous monitoring of cybersecurity risks.
Continuous penetration testing helps close that gap. Instead of treating testing as a one-time event, it becomes part of an ongoing security program that gives you regular insight into what has changed, what matters most, and where to focus remediation efforts next.
For organizations that need more than a yearly snapshot, continuous testing provides a more practical way to manage exposure over time.
What is Continuous Penetration Testing?
Continuous penetration testing is an ongoing approach to security testing that combines recurring assessment, validation, and prioritization to identify vulnerabilities before attackers can exploit them.
At Rootshell, continuous penetration testing is delivered through a service model that blends:
automated discovery and scanning for scale
human-led penetration testing where validation matters
attack surface visibility across internet-facing assets
prioritization and remediation workflows through the Rootshell Platform
measurable progress over time instead of a single static report
This gives security teams a clearer view of real-world exposure and a more operational way to reduce risk continuously.
How Rootshell Delivers Continuous Testing
Continuous penetration testing is not just about running scans more frequently. It requires a structured approach that combines automation, expert validation, and operational workflows to ensure vulnerabilities are identified, prioritized, and remediated continuously.
Rootshell delivers this through a tiered continuous testing model, designed to support organizations at different levels of security maturity. Instead of a single annual engagement, testing becomes an ongoing program that evolves alongside your environment.
The comparison below shows how Rootshell’s continuous testing services extend beyond traditional penetration testing, providing greater visibility, validation, and operational support throughout the year.
Across all tiers, results are delivered through the Rootshell Platform, providing a centralized view of vulnerabilities, remediation progress, and testing activity.
Continuous testing levels
Choose the level of testing that fits your business
Every level is human-led, delivered through the Rootshell Platform, with free retests. Start where you are and step up as your needs grow.
- Manual baseline test and dynamic scoping
- Automated testing on a schedule through the year
- AI Exploit Detection Service
- Remediation Workflows and SLA Tracking
- Automation Centre
- Complimentary ASM scan
- Dedicated account manager
- Platform access, customer success and free retests
- Everything in Core
- Test results validated by our testers
Compare the levels
| Feature | Traditional testtypical | CoreContinuous Testing | ManagedContinuous Testing |
|---|---|---|---|
| Duration | 5 days | 12 months | 12 months |
| Testing frequency | One-off | Daily, weekly or monthly | Daily, weekly or monthly |
| Continuous testing type | Not applicable | Automated, unauthenticated | Manual and automated |
| Manual baseline test | ✓Included | ✓Included | ✓Included |
| Authenticated testing | ✓Included | ✓Included manual baseline test | ✓Included |
| Dynamic scoping | ✓Included | ✓Included | ✓Included |
| Test results validated by our testers | –Not included | ✓Included manual baseline test | ✓Included |
| Free remote retests | –Not included | ✓Included | ✓Included |
| Exploit intelligence for the whole contract term, so issues are reprioritised | –Not included | ✓Included | ✓Included |
| Remediation workflows | –Not included | ✓Included | ✓Included |
| Automation Centre | –Not included | ✓Included | ✓Included |
| SLA tracking | –Not included | ✓Included | ✓Included |
| Complimentary ASM scan | –Not included | ✓Included | ✓Included |
| Unlimited access to the Rootshell Platform | –Not included | ✓Included | ✓Included |
| Customer success support | –Not included | ✓Included | ✓Included |
| Dedicated account manager | –Not included | ✓Included | ✓Included |
The traditional column describes a typical one-off engagement; providers differ.
How much does continuous penetration testing cost?
Rootshell Core starts from £3,000 plus VAT a year for one public-facing web application. That covers an authenticated manual test, validated by our testers, followed by 12 months of automated, unauthenticated continuous testing, run daily, weekly or monthly. A one-off manual test of the same application typically costs between £3,000 and £10,000 before VAT, so continuous testing does not have to cost more than an annual test.
| One-off annual test | Rootshell Core | |
|---|---|---|
| Typical cost | £3,000 to £10,000 before VAT (indicative, one public-facing web application) | From £3,000 plus VAT a year |
| When you are tested | Once, in a fixed window | An authenticated manual test, then automated, unauthenticated continuous testing through the year, run daily, weekly or monthly |
| How you get results | Varies by provider | The Rootshell Platform, kept current for 12 months |
| Retests | Varies by provider | Free and remote for issues found in Rootshell testing |
Your price depends on the number of applications, the type of test and the size and complexity of your environment, and is confirmed after a short scoping call. See Rootshell pricing
The £3,000 to £10,000 range is indicative and is not a quote. Last reviewed 9 November 2026.
The benefits of continuous pen testing
Bolster your security strategy and ensure year-round protection with continuous security testing.
Reduce exposure faster
Identify and validate issues earlier so your team can prioritize remediation before weaknesses accumulate.
Keep up with change
As your infrastructure, applications, and internet-facing assets evolve, your testing program evolves with them.
Improve remediation efficiency
A continuous model helps teams focus on the highest-value actions instead of revisiting outdated findings months later.
Strengthen audit and board reporting
Show ongoing testing activity, progress over time, and clearer evidence of how risk is being reduced.
Move beyond static reports
Replace one-time deliverables with a more operational view of security posture and remediation progress.

Why Organizations Choose Rootshell?
We’re proud to be a trusted provider of continuous security testing for some of the UK’s largest organizations.
Continuous by Design
Our service is built for organizations that want security testing embedded into an ongoing program, not treated as a yearly event.
Platform-backed delivery
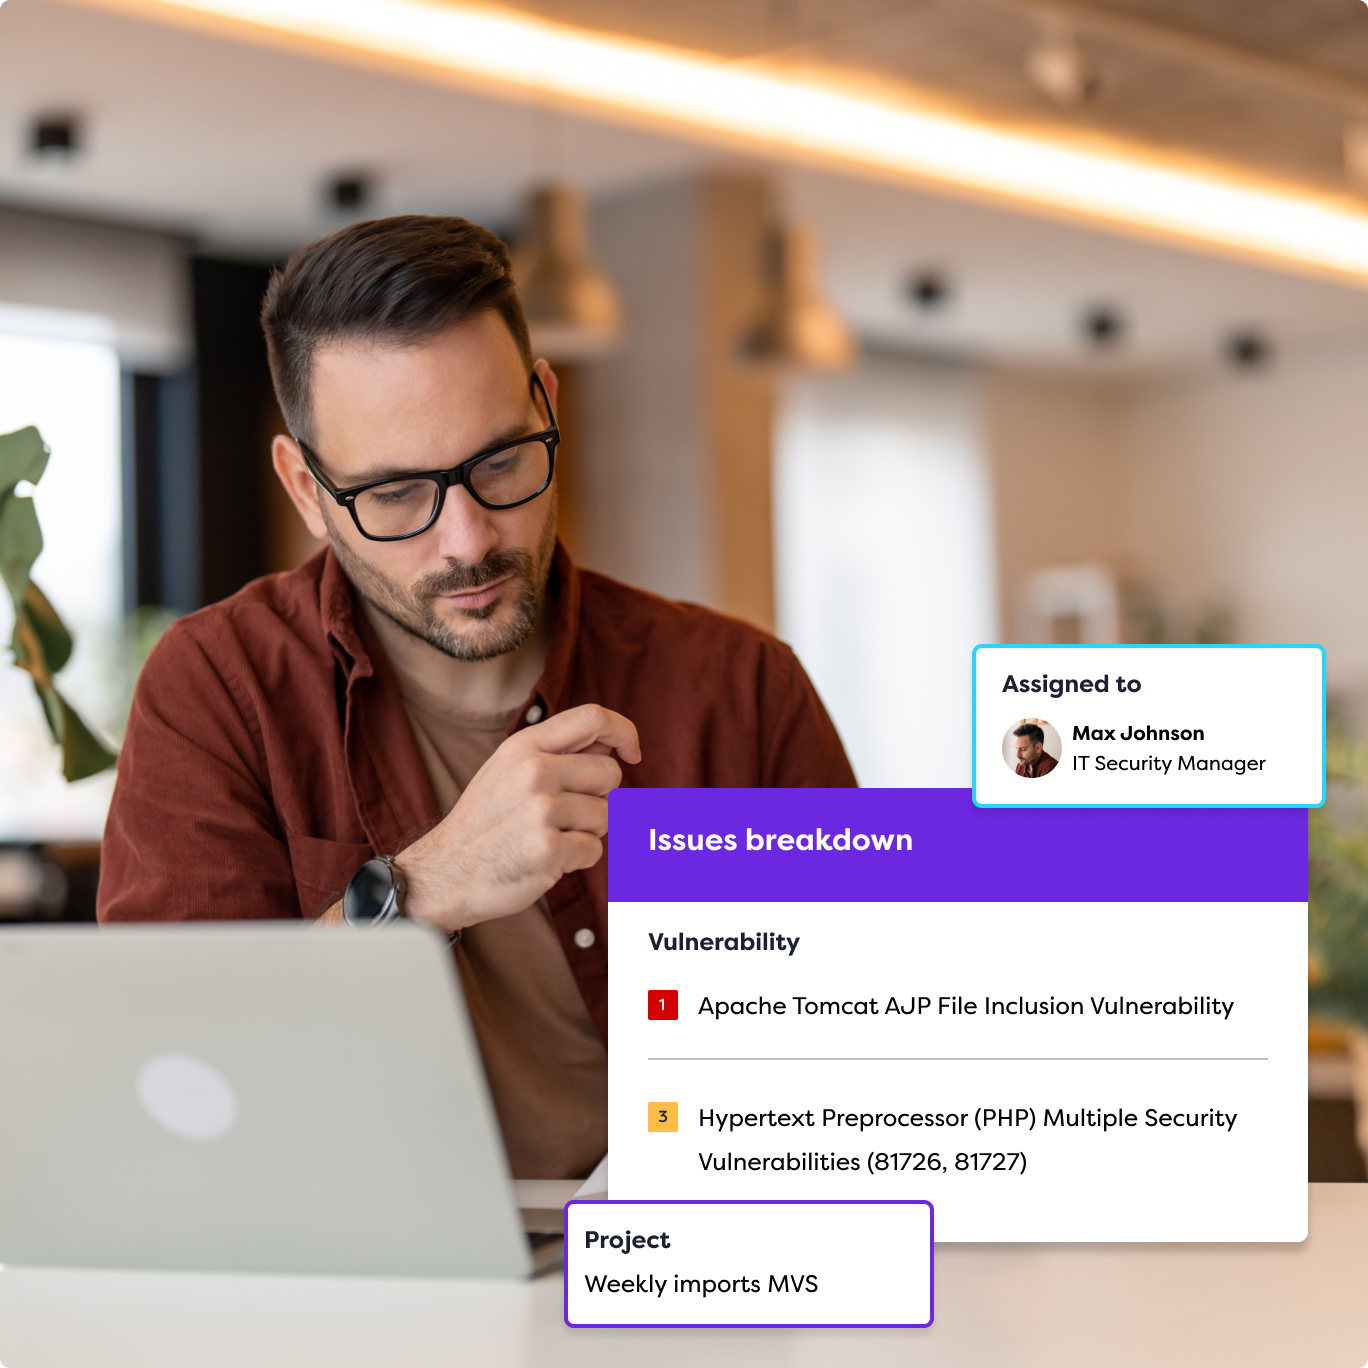
The Rootshell Platform gives your team a central place to manage findings, track remediation, and maintain visibility across testing activity.
Automation plus expert consultancy
We combine the scale of automation with the judgment of experienced security consultants to give you broader coverage and better decision-making.
Built for operational teams
We help teams move away from fragmented reporting and spreadsheet-led processes toward a more structured and measurable model.
CREST-aligned expertise
Our testing is delivered to recognized industry standards, with experienced practitioners who understand both technical validation and practical risk reduction.
Trusted by Security Teams That Need More Than a PDF

Frequently asked questions
Can’t find the answer to your question? You can always contact our team of experts for a chat!
What is continuous penetration testing?
Continuous penetration testing is an ongoing approach to security testing that combines recurring assessment, validation, and remediation support to reduce cyber risk over time.
How is continuous penetration testing different from annual penetration testing?
Annual penetration testing provides a point-in-time snapshot. Continuous penetration testing provides ongoing visibility, validation, and prioritization as your environment changes.
Is continuous penetration testing the same as PTaaS?
No. PTaaS (Penetration Testing as a Service) is a service delivery model, while continuous penetration testing describes the ongoing testing approach.
Does continuous penetration testing replace manual testing?
No. The strongest continuous testing programs combine automation for scale with human-led testing for validation, context, and exploitation.
Who is continuous penetration testing best suited for?
It is especially useful for organizations with changing environments, external attack surface growth, ongoing remediation demands, or a need for clearer year-round visibility.
Can continuous penetration testing support compliance requirements?
Yes. While compliance needs vary, continuous penetration testing can support organizations that need recurring evidence of testing activity, remediation progress, and risk management.