The Rootshell Platform continues to evolve — and this month’s update brings EPSS-driven prioritization, a conversational way to query your vulnerability data, and a set of workflow improvements designed to make exposure management smarter, faster, and more accurate across every layer of your security operations.
From exploit likelihood scoring and the new Rootshell Platform MCP Server (beta) to automatic vulnerability categorisation, richer exports, faster host lists, and refined partner dashboards, these updates reinforce Rootshell’s commitment to delivering intelligent, enterprise-scale security management.
EPSS: Know What Attackers Are Likely to Exploit Next
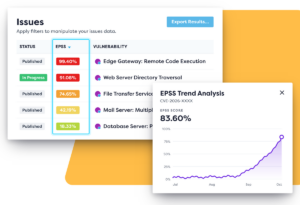
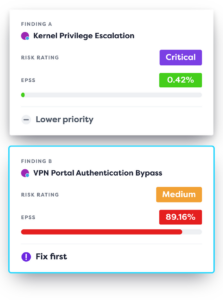
Not every critical vulnerability gets exploited, and not every medium is safe. Rootshell now adds the Exploit Prediction Scoring System (EPSS) to the platform, giving every vulnerability a daily, data-driven estimate of how likely it is to be exploited in the wild within the next 30 days.Combined with severity, exploit intelligence and asset context, EPSS helps your team put effort where it will reduce the most real-world risk.
The platform retrieves EPSS data every day and matches it to the CVEs in the vulnerability database, storing both the EPSS score and percentile with a daily history for every CVE.
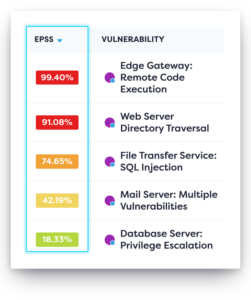
EPSS appears as a colour-coded percentile badge in the Issues table, Phase Issues table, Issue view and Affected Instances table. Where an issue has multiple CVEs, the highest EPSS-rated CVE is shown, so you always see the worst case.
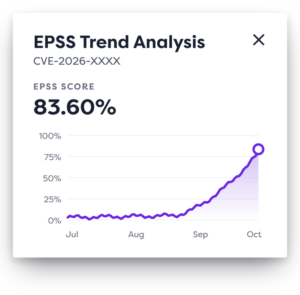
From within an issue, click a CVE entry to open the EPSS Trend Analysis and see whether the likelihood of exploitation is rising, falling or holding steady.
Key highlights:
- Smarter prioritization: focus on what attackers are most likely to go after, not just the highest CVSS.
- Fewer wasted cycles: safely de-prioritise high-severity findings with a very low likelihood of exploitation.
- A defensible story: a clear, industry-standard reason for why a finding was escalated.
- Fully configurable: on by default, sortable, exportable, and can be shown or hidden with column controls.
- Available in the API: score, percentile, last-updated timestamp and driving CVE are returned through the Issue and Affected Instance APIs. Values are null where no EPSS data exists, so existing integrations are unaffected.
This enhancement gives auditors, executives and clients a clear reason for every escalation decision, while keeping teams focused on real exposure.
Rootshell Platform MCP Server (Beta): Talk to Your Vulnerability Data
What if you could simply ask your vulnerability data a question? The new Rootshell Platform MCP Server, now in beta, lets you connect any AI assistant or tool with an MCP client to the platform using the Model Context Protocol (MCP), an open standard for connecting AI tools to data sources.
It has been tested with ChatGPT, Microsoft Copilot, Claude and Gemini. Ask in plain English and get answers drawn from your own Rootshell data.
Access is read-only by design, built on the platform’s read (GET) API endpoints, so assistants can retrieve and analyse data but cannot modify it or take remediation actions. Connections are authorised through an OAuth 2.0 sign-in, an assistant can only see the tenant and data your own user is already permitted to see, and each tenant has its own MCP server address. Microsoft Copilot Studio agents can also be shared with teams through Microsoft Teams and Microsoft 365 Copilot.
For security partners: MSSPs and consultancies can use the same capability to prepare for client reviews, quarterly business reviews and executive briefings in seconds rather than hours — without changing how the platform is used.
Example prompts:
- Show me all currently open critical issues.
- Which open issues have an active exploit?
- Which assets have the highest number of critical and high-severity issues?
- What should I prioritise for remediation?
The MCP Server is currently in beta and is enabled per tenant for participating clients. Contact your Rootshell representative to request access; setup guides for Claude, ChatGPT and Microsoft Copilot Studio are available in the Knowledge Base.


Vulnerability Categorisation Engine (Stage 1)
Stage one of the Vulnerability Categorisation Engine is now underway. Working quietly in the background, every vulnerability entering the Vulnerability Database is automatically assigned a primary category during ingestion, consistently across all supported sources.
For example, a Windows security update is grouped with operating system patching, while a cross-site scripting finding is grouped with web application vulnerabilities.
Deterministic, configurable rules evaluate titles, descriptions, remediation text, CVEs, vendor and product details, scanner metadata, ports, services and protocols, with a fixed priority order when several rules match.
Key highlights:
- Consistent categorisation across every supported source.
- Category, confidence score, classification source, matched rule and keyword, rule version and timestamp stored for each vulnerability.
- All category data exposed through the platform APIs.
- Nothing to configure and no change to how you work today.
This stage builds the foundation. The front-end experience is coming soon, putting categories to work in dashboards and reports and enabling category-driven remediation guidance — for example, rolling many Apache version findings into one action: upgrade Apache.
Quick Import: Set Confirmed At and Published At Dates
Importing historic data shouldn’t mean exporting, editing a JSON file and re-importing just to get your SLA dates right. Quick Import now lets you set the dates yourself.
Confirmed At is now a clear date/time picker, replacing the old Select control, so you can record when the issue was actually identified by the source. Published At is a, optional date picker that is used for dashboards and SLA tracking; leave it blank and the standard publish timestamp.
Helpful tooltips explain each field, and the Quick Import layout has been refreshed with clearer steps and better grouping of import settings.
Why it matters:
- Accurate SLAs from day one: the SLA clock starts from the date you intend, not the date you uploaded.
- Trustworthy trending: historic imports feed remediation trends and dashboard metrics from the right point in time.
- Ideal for migrations: bring in reports from previous weeks, months, or another platform without distorting reporting.
- Less manual effort for teams who receive vendor reports after the test was completed.
Where to find it: the Quick Import workflow when importing scan results into a project.
Filter by Null Values
Housekeeping just got a lot easier. You can now filter for items where a value is empty, so finding unassigned or untagged work is a one-step job.
Where to find it:
- Results > Issues: Tags = Null, User Assigned = Null.
- Results > Assets: Tags = Null, System Owner = Null, Technical Owner = Null.
Quickly assign unassigned issues in bulk, spot assets with no tags or no owner to close governance gaps, and stop sorting columns or exporting to Excel just to find blanks.
Faster Phase-Level Host Lists
Phases containing thousands of hosts, such as large Microsoft Defender imports, now load and sort much faster.
Host pages are designed to load much quicker, even with more than 1,000 hosts, with issue counts retrieved separately so ordering stays responsive.
Key highlights:
- Faster loading and sorting for large phases.
- A more responsive experience for enterprise-scale imports.
- Where to find it: Projects > Phase > Hosts.
Less waiting, more reviewing — even in the biggest environments.
Export Issues: More Data in Every Export
The asset issue export, now named Export Issues, includes every available column plus additional detail, so findings reach other teams, reports and tools with the full picture.
Columns now included:
- Status, First Seen, Last Seen, Reference, Vulnerability, Summary.
- Technical Details, Recommendations, CVE, References.
- Project, Assigned, Hostname, IP Address, Port, Service, Tags.
- Remediation Deadline and SLA.
This gives teams a richer, more complete export without extra steps or manual combining of files.