Test how well your defenders detect and respond to a realistic attack

Purple team, simulated attack and adversary emulation assessments that test your people, process and technology together.

Trusted by companies of all shapes and sizes

What are purple team and adversary emulation assessments?

Where a red team tests whether an attacker can get in, these assessments test how well you detect and respond. A purple team works openly with your defenders, running attacker techniques step by step so detections can be checked and improved on the spot.

Adversary emulation and simulated attack assessments reproduce the documented behaviour of real threat actors, mapped to frameworks such as MITRE ATT&CK, so you can see which techniques your controls catch and which they miss. Detection gaps are recorded in the Rootshell Platform. Our testers stop and ask you first before taking any step further than agreed.

The benefits of purple team and adversary emulation for your business

See which attacker techniques your controls catch and which they miss.

Identify vulnerabilities
Identify detection gaps

Find the attacker techniques your monitoring and tooling do not see, and the alerts that fire too late to matter.

Prepare for a real-world attack
Proactive defence

Improve detections with your defenders in the room, so fixes are made and checked straight away.

CREST-certified pen testing
Rehearse your response

Exercise your incident response with realistic activity, so your team has practised before it counts.

Insight
Better visibility and control

Map results to MITRE ATT&CK and track detection improvements over time.

Comply_with_security_standards (1)
Stay compliant

Provide evidence of tested detection and response for customers, boards and regulators.

Stay ahead of threats with our purple team and adversary emulation

Get Started

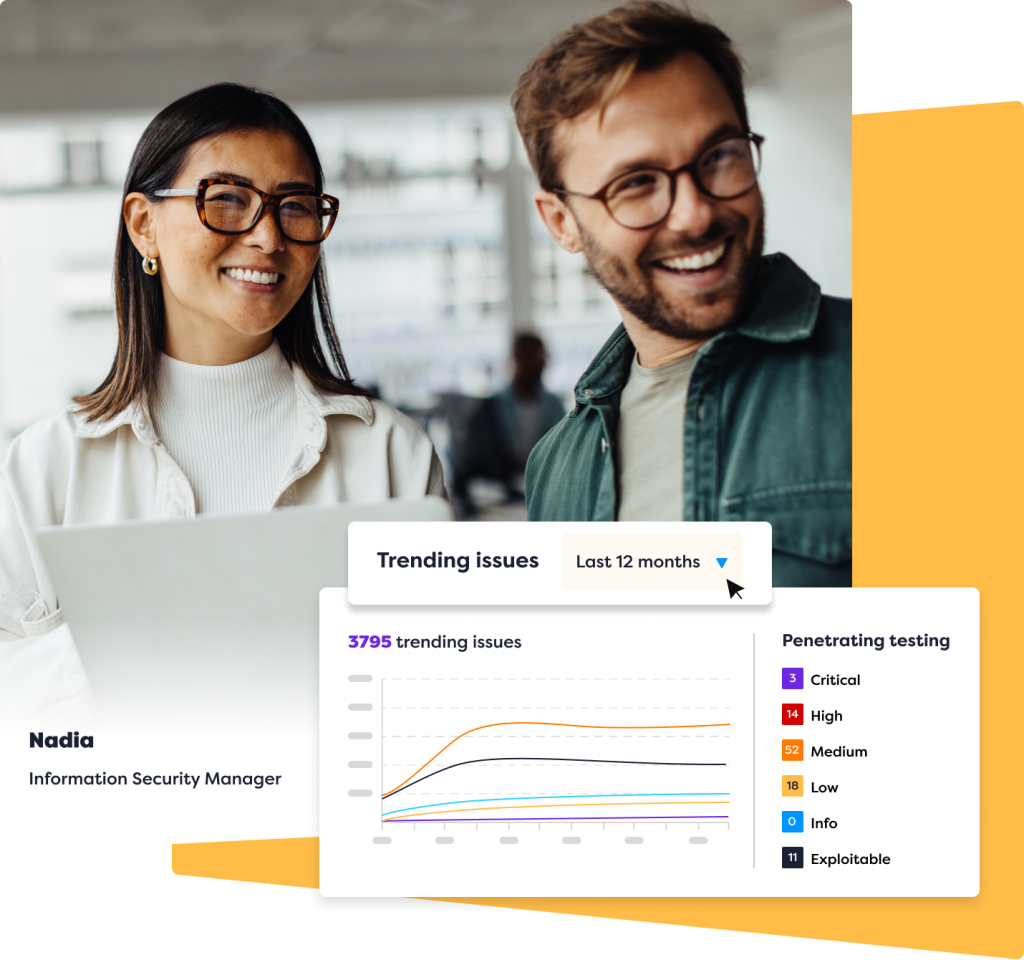
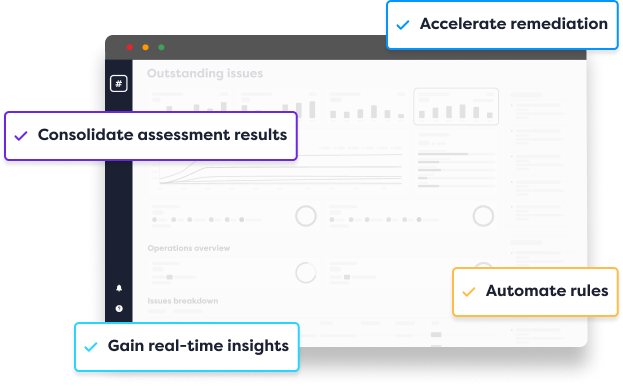
On-demand purple team results at the click of a button

The Rootshell Platform is a neutral, centralised hub for managing vulnerabilities and protecting against threats, providing you with a single source of cyber security truth.

Recognised industry leader in penetration testing as a service (PTaaS)

Comprehensive purple team and adversary emulation tailored to your needs

Elevate your security with a customisable, all-in-one solution tailored to your unique objectives, risk appetite, and budget.

Rootshell PTaaS package

12-month contract
Build your package:

Plus receive your results an data through The Rootshell Platform

Ready to get started?

Discover your needs

Share your security requirements with us, and Rootshell will follow up to ensure we’re the perfect fit for your organisation.

Dive into a personalised demo

Experience a tailored demonstration of our vulnerability management platform, showcasing how it can enhance your security posture.

Seamless onboarding

Start using the Rootshell platform, input previous vulnerability data, and get solutions tailored to your team’s goals, risk appetite, and budget.

Reasons to work with us

For purple team and adversary emulation, Rootshell combines accredited testers with the Rootshell Platform, so every finding is easy to track and fix.

Powered by our platform
All your results in one place

Findings, retests and fixes sit in the Rootshell Platform alongside your other testing and scanner results, so progress is easy to track.

CREST-certified pen testing
Accredited, experienced testers

Delivered by experienced testers. Rootshell is CREST registered, Cyber Scheme accredited, ISO 27001 certified, an IASME Cyber Essentials Plus certification body, and NCSC CHECK scheme accredited.

Quality assured
Recognised standards

Techniques can be mapped to MITRE ATT&CK so detection gaps are easy to see and track.

Expert advice and support
Clear reports, clear next steps

Clear, prioritised findings with practical fix advice, and retesting to confirm that fixes have worked.

Remote penetration testing
How we deliver it

Scope, objectives and timing are agreed with you first, and your defenders can work alongside the testers.

Talk to our team about purple team and adversary emulation

Book a demo

Don’t just take our word for it, hear what our customers think

Purple team compared with red team

Purple teamRed team
StyleTesters and your defenders work togetherTesters work separately, often without warning
Main aimImprove detection and response as you goTest how well you spot and stop an attack
OutputTuned detections and clear next stepsA picture of how far an attacker could get
Best forTeams building their detection skillsTeams ready for a full test of their defences

Common questions about purple team and adversary emulation

What is a purple team exercise?

It is a joint exercise where testers simulate attacker behaviour while your defenders watch and tune their detection, so both sides learn at the same time.

What is adversary emulation?

It is testing that follows the methods of known attackers, so you can see how your defences cope with realistic behaviour.

How is it different from a red team?

A red team test is usually kept quiet to test your response. A purple team exercise is open, so you can improve in real time.

Who should be involved?

Your security operations and IT teams, and anyone who owns detection tools.

Last reviewed: 5 November 2026. Written and reviewed by the Rootshell R&D team. Rootshell was founded six years ago and is founder-led, drawing on more than 30 years of industry experience from previous successful businesses. We deliver thousands of testing days every year. CREST registered, Cyber Scheme accredited, ISO 27001 certified, an IASME Cyber Essentials Plus certification body, and NCSC CHECK scheme accredited.

Related testing services

Most clients combine more than one test. These pair well with purple team and adversary emulation.

Ready to take back control of your cyber security?

    Talk to us

    We use your details to reply to you. See our Privacy Policy