Find the weaknesses in your mobile apps and devices before attackers do
Mobile application and device testing that shows how your apps, handsets and management controls stand up to a real attacker.
Trusted by companies of all shapes and sizes
What is mobile application and device testing?
Mobile testing examines the apps your customers and staff install, the devices they run on, and the services behind them. Our testers review iOS and Android applications, how data is stored and transmitted, and how the app talks to its back-end APIs.
We also assess the devices themselves, including Apple iOS configuration and your mobile device management (MDM) set-up, so you can see whether a lost, stolen or compromised handset could expose company data. Every issue is reported in the Rootshell Platform with a clear severity and remediation advice.
The benefits of mobile application and device testing for your business
See your mobile estate the way an attacker does, and fix what matters first.
Identify potential vulnerabilities
Find weaknesses in app code, local data storage, authentication, session handling and the APIs your apps rely on.
Proactive defence
Check that your mobile controls work in practice, not just on paper, including how apps behave on a device that has been tampered with.
Prepare for loss and compromise
Understand what an attacker could reach from a lost, stolen or compromised handset, and whether your MDM policies limit the damage.
Better visibility and control
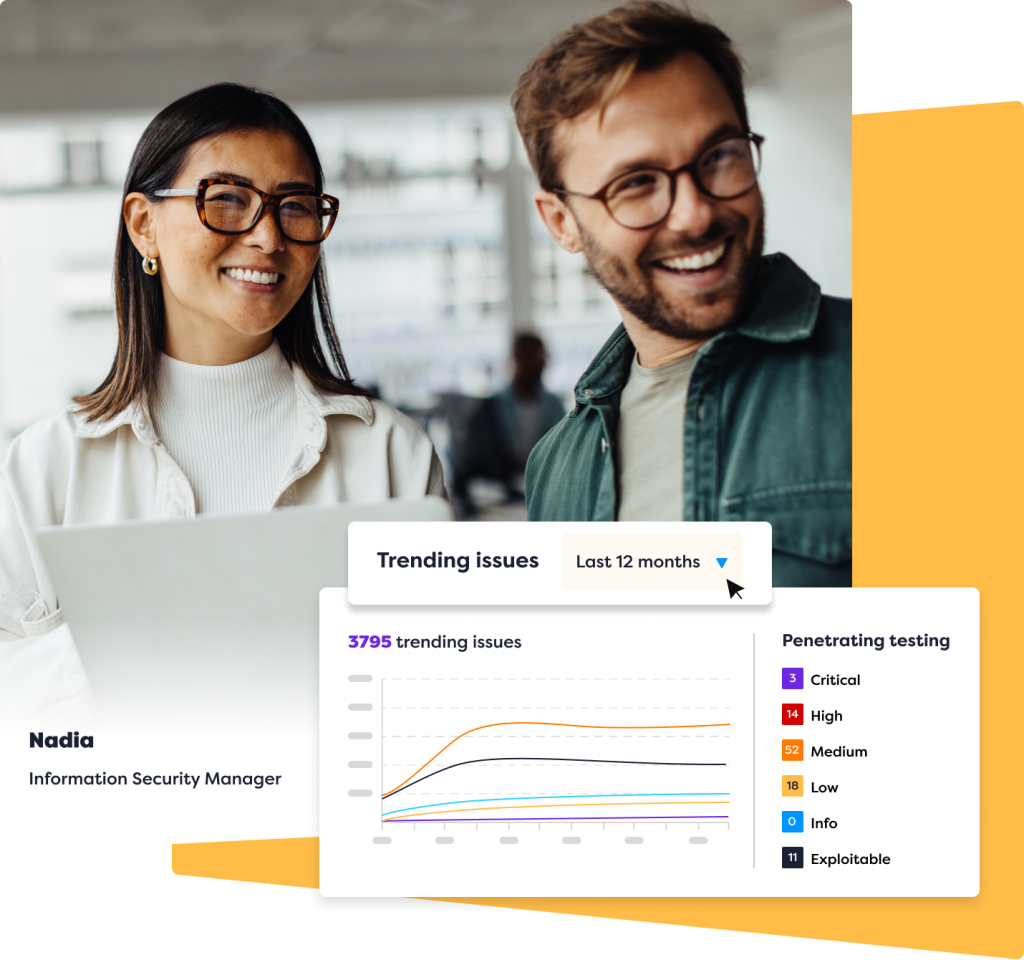
Findings land in the Rootshell Platform, prioritised by severity and by how important the affected app or device is to your business.
Stay compliant
Provide evidence for customer, audit and regulatory requirements that expect regular testing of mobile apps handling sensitive data.
Stay ahead of threats with our mobile application and device testing
Get Started
On-demand mobile testing results at the click of a button
The Rootshell Platform is a neutral, centralised hub for managing vulnerabilities and protecting against threats, providing you with a single source of cyber security truth.
Recognised industry leader in penetration testing as a service (PTaaS)
Comprehensive mobile application and device testing tailored to your needs
Elevate your security with a customisable, all-in-one solution tailored to your unique objectives, risk appetite, and budget.
Build your package:
- Penetration Tests
- Managed Vulnerability Scanning (MVS)
- Attack Surface Management (ASM)
- Red Team Assessments
- We help you choose the services that best fit your needs
- Solutions tailored to meet your team’s objectives, risk appetite, and budget
Plus receive your results an data through The Rootshell Platform
Ready to get started?
Discover your needs
Dive into a personalised demo
Seamless onboarding
Reasons to work with us
For mobile application testing, Rootshell combines accredited testers with the Rootshell Platform, so every finding is easy to track and fix.
All your results in one place
Findings, retests and fixes sit in the Rootshell Platform alongside your other testing and scanner results, so progress is easy to track.
Accredited, experienced testers
Delivered by experienced testers. Rootshell is CREST registered, Cyber Scheme accredited, ISO 27001 certified, an IASME Cyber Essentials Plus certification body, and NCSC CHECK scheme accredited.
Recognised standards
Testing draws on recognised guidance for mobile apps, such as the OWASP Mobile Application Security Verification Standard.
Clear reports, clear next steps
Clear, prioritised findings with practical fix advice, and retesting to confirm that fixes have worked.
How we deliver it
Scope, access and timing are agreed with you before testing starts, and delivery can be remote or on site where the test allows.
Talk to our team about mobile application testing
Book a demo
Don’t just take our word for it, hear what our customers think
Mobile application testing compared with automated mobile scanning
| Mobile application testing | Automated mobile scanning | |
|---|---|---|
| What it looks at | The app itself, data stored on the device, network traffic and the back-end services it calls | Known patterns and common misconfigurations |
| Business logic | Tested by a person who tries to misuse the app | Rarely covered |
| Findings | Checked by a tester before you see them | Often need triage to remove false alarms |
| Best used | Before release and after major changes | Between tests, as a regular baseline |
Common questions about mobile application testing
What does mobile application testing cover?
We test iOS and Android apps, including how they store data on the device, how they communicate over the network, how users log in, and the back-end APIs they depend on.
How is it different from mobile device testing?
Application testing looks at one app. Device testing looks at how a phone or tablet is set up and managed, for example through mobile device management (MDM).
Do you need the source code?
Not always. Many tests start from the app build. Sharing source code can add depth and is worth discussing when we scope the work.
How often should a mobile app be tested?
At least before release and after significant changes. With Rootshell Continuous Testing, changes can be tested through the year, and the results sit in the Rootshell Platform.
Last reviewed: 5 November 2026. Written and reviewed by the Rootshell R&D team. Rootshell was founded six years ago and is founder-led, drawing on more than 30 years of industry experience from previous successful businesses. We deliver thousands of testing days every year. CREST registered, Cyber Scheme accredited, ISO 27001 certified, an IASME Cyber Essentials Plus certification body, and NCSC CHECK scheme accredited.
Related testing services
Most clients combine more than one test. These pair well with mobile application and device testing.